Key migration
This procedure describes how to migrate keys from Key Trustee Server to Ranger KMS.
- Locate the keys in Key Trustee Server.
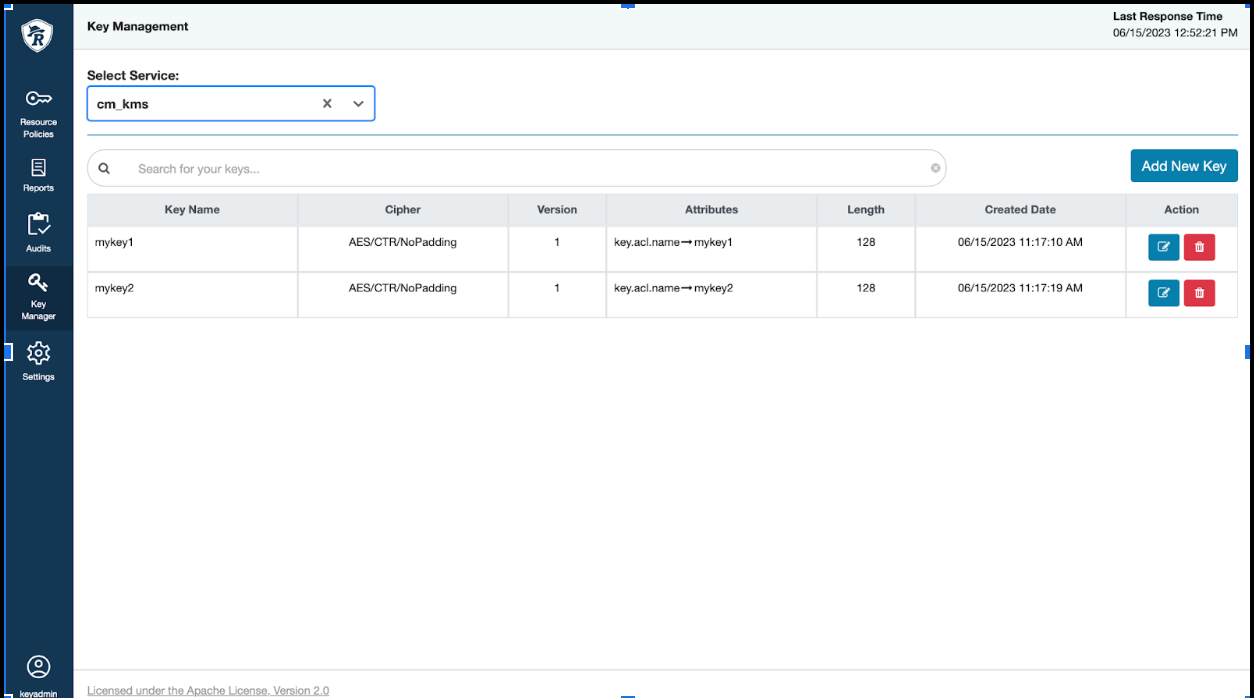
- Login to Ranger UI with Key Admin credentials.
- Go to , to view the HDFS encryption zone keys with service
Ranger KMS KTS.
- If Navigator Encrypt is setup, locate its keys.
- SSH in to the active KTS node.
- Login to Postgres 14 database for Cloudera Runtime version 7.1.9.
- The 'keytrustee' user is created with 'nologin' by default. Update
the keytrustee user in /etc/passwd before
accessing the database by running the following command:
sed -i "/keytrustee:x:$( id -u keytrustee ):$( id -g keytrustee ):Keytrustee User:\/var\/lib\/keytrustee:\/sbin\/nologin/c\keytrustee:x:$( id -u keytrustee ):$( id -g keytrustee ):Keytrustee User:\/var\/lib\/keytrustee:\/bin\/bash" /etc/passwd - Run the following commands:
select handle from deposit;For Cloudera Runtime version 7.1.9:
# sudo -u keytrustee LD_LIBRARY_PATH=/opt/cloudera/parcels/KEYTRUSTEE_SERVER/PG_DB/opt/postgres/14.2/lib /opt/cloudera/parcels/KEYTRUSTEE_SERVER/PG_DB/opt/postgres/14.2/bin/psql -p 11381 keytrustee

keytrustee=# select handle from deposit;
handle
---------
mykey1
mykey2

control

control
(6 rows)
-
Backup the KTS database.
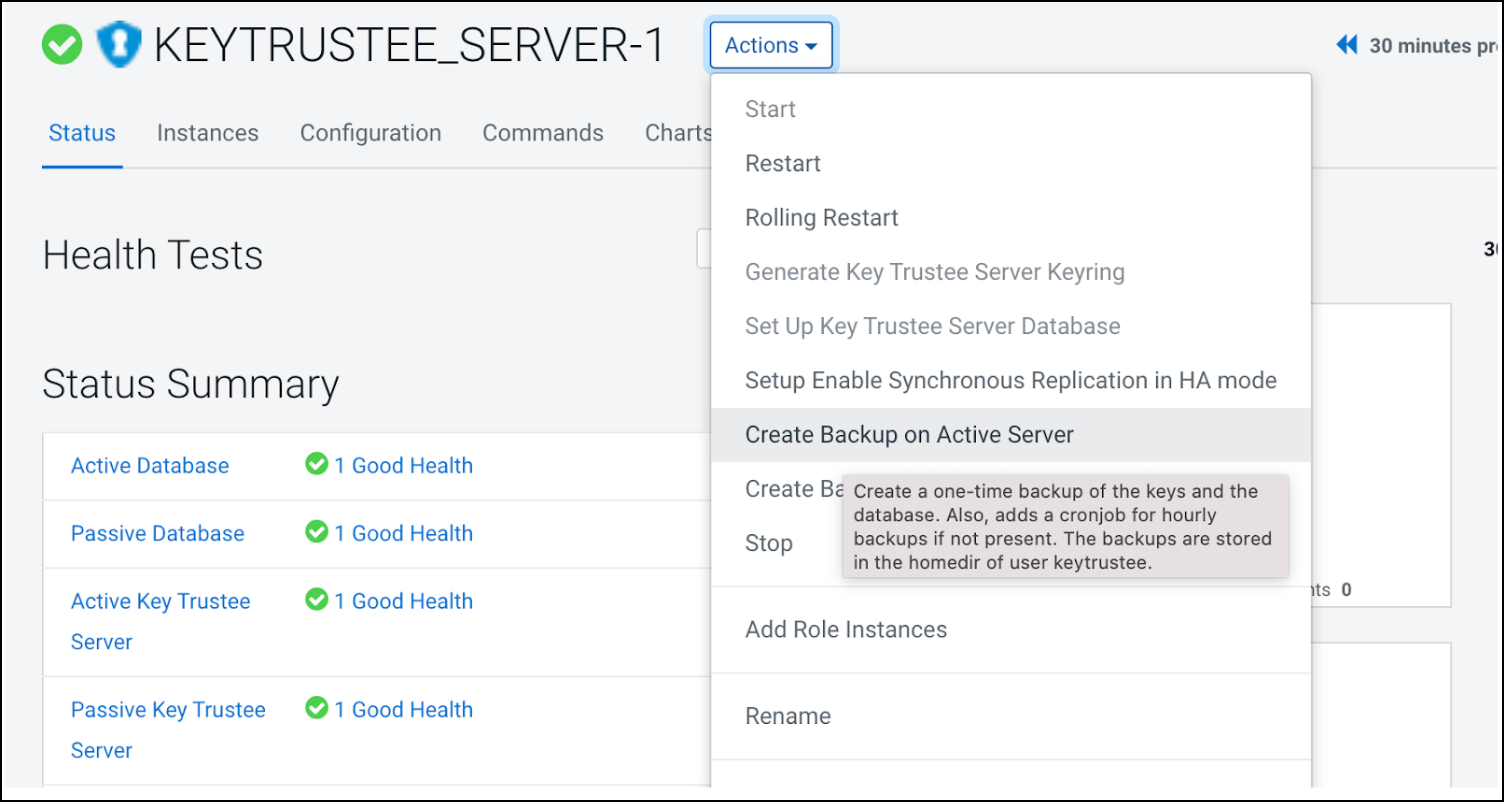 The backup will be created at /var/lib/keytrustee/ on Active KTS node.
-
Export the Navigator Encrypt keys.
-
Go to .
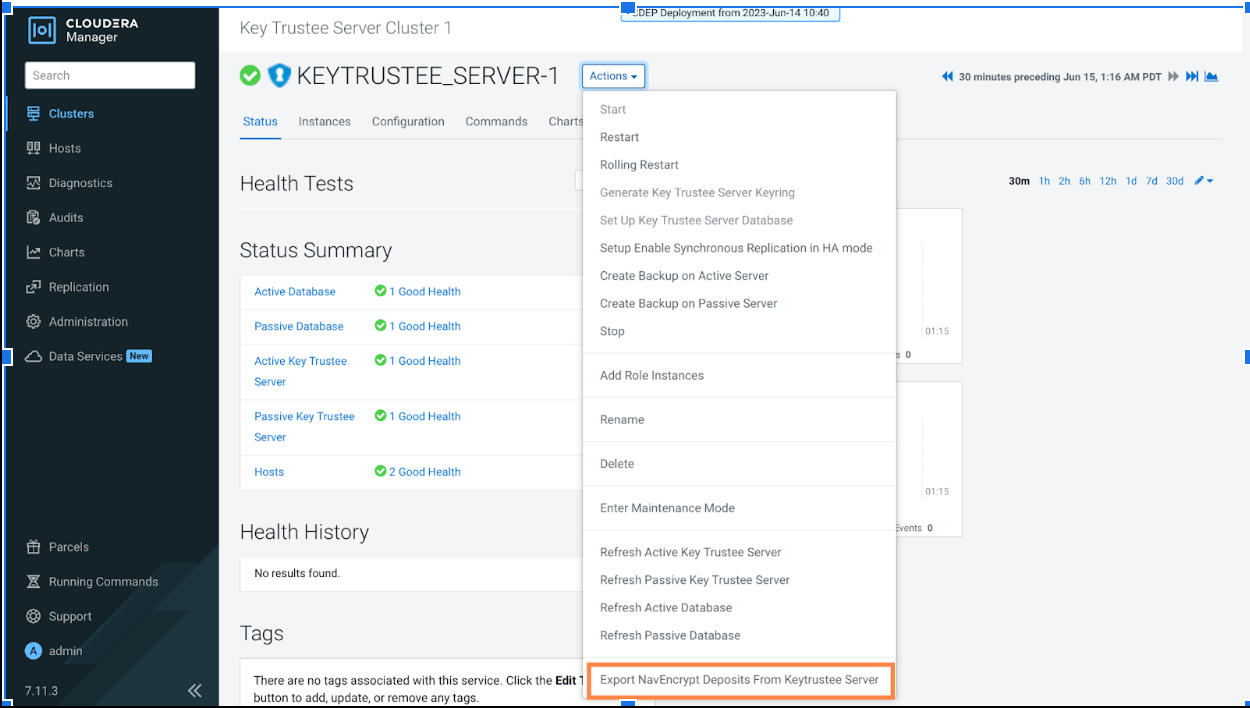 This will generate the CSV required to import Navigator Encrypt keys in Ranger KMS DB after migration. The deposits.csv file will be created at /var/lib/keytrustee/.keytrustee.
-
Go to .
-
Back up the Ranger KMS KTS directory and generate a keystore file of existing encryption zone keys.
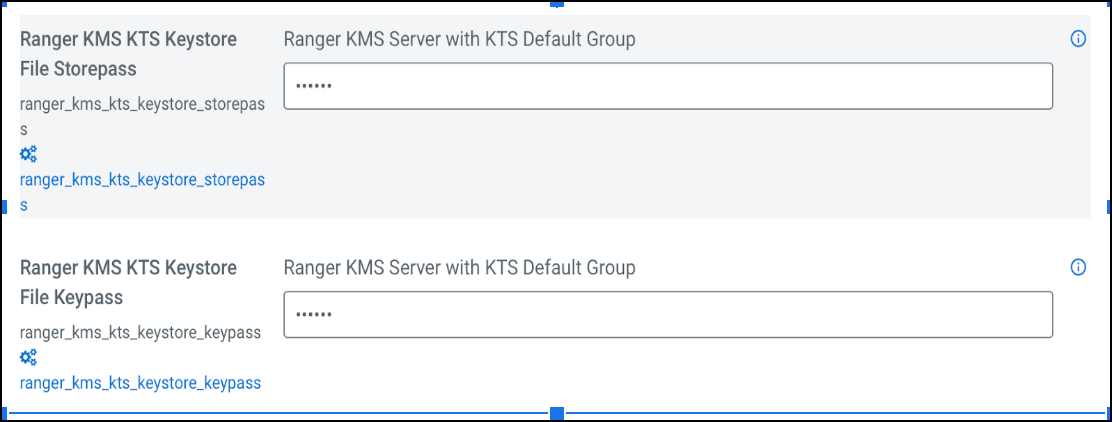
The keystore file is protected using Store password (default value: mystorepass) and Key password (default value: mykeypass), that are configurable in RANGER KMS KTS configuration.
-
Go to and select
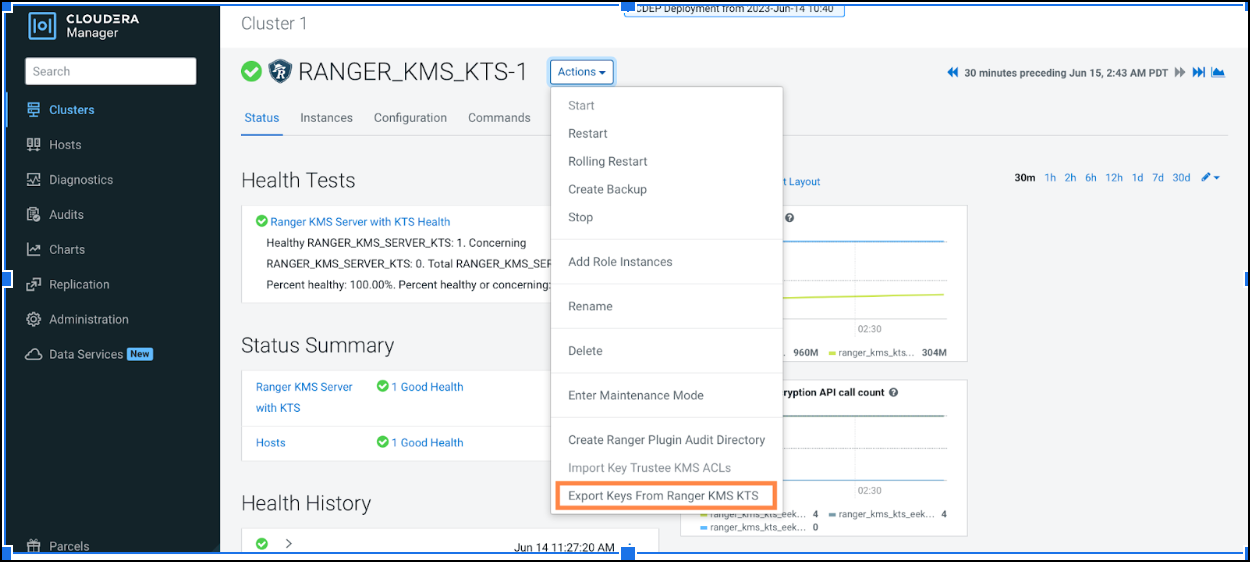
The service GPG keys backup and keystore file will be created at /var/lib/kms-keytrustee on Ranger KMS KTS node. -
Go to and select
-
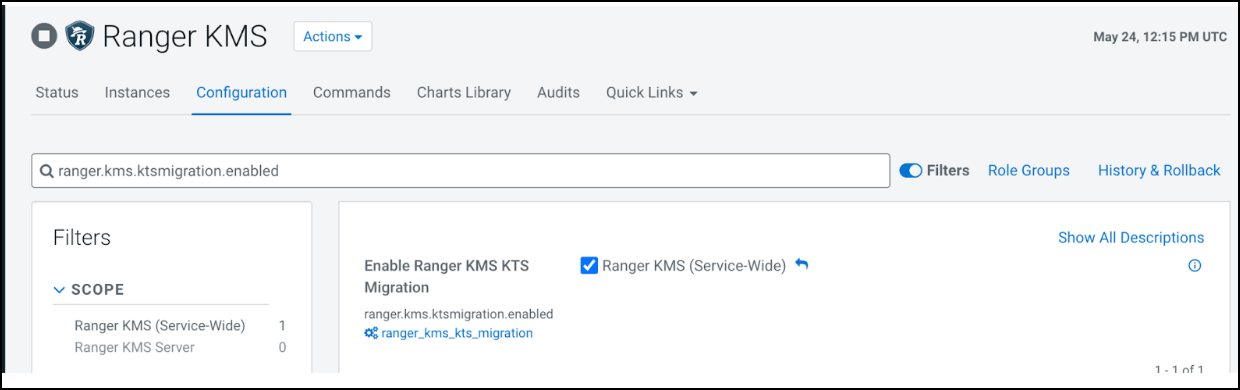
Enable the migration flag and complete the wizard.
-
Go to and check .
-
Go to and check .
-
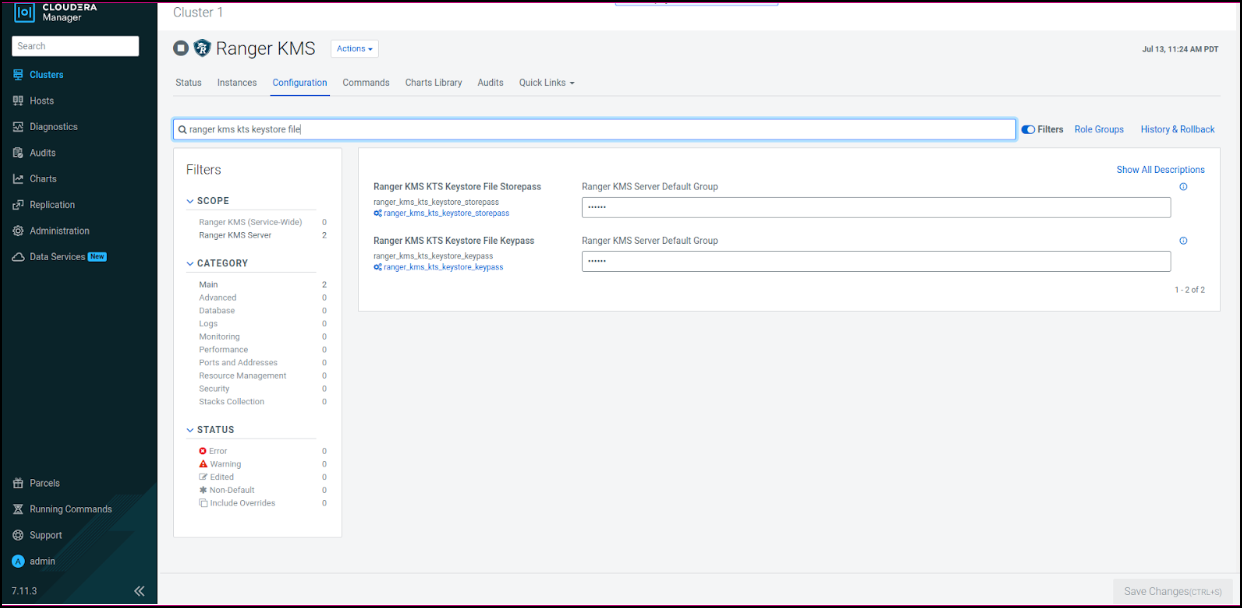
Configure the Key password (default value: mykeypass) and Store password
(default value: mystorepass) in Ranger KMS configuration.
These are the same passwords that were configured in Step 3 in Ranger KMS KTS.
-
If Navigator Encrypt is configured on the cluster, copy
deposits.csvfile to the Ranger KMS node, and grant permission kms:kms.The location is configurable using the propertyKey Trustee NavEncrypt Keys Full Path.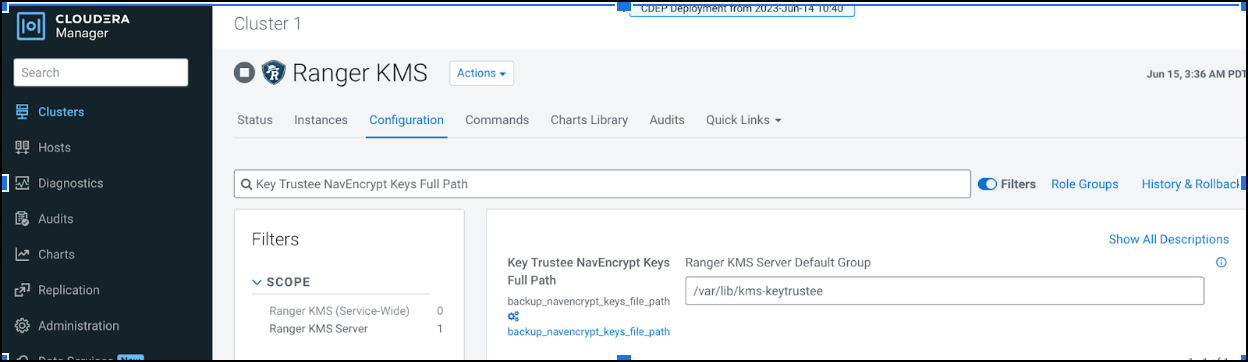
 # scp root@dsktstokms-4.vpc.cloudera.com:/var/lib/keytrustee/.keytrustee/deposits.csv /var/lib/kms-keytrustee
                                                                                                                                                              100%   10KB   8.2MB/s   00:00
 # ls -ltr /var/lib/kms-keytrustee/deposits.csv
 -rw-r--r-- 1 root root 10401 Jun 15 03:34 /var/lib/kms-keytrustee/deposits.csv
 # chown kms:kms /var/lib/kms-keytrustee/deposits.csv
 # ls -ltr /var/lib/kms-keytrustee
 total 64
 -rw-r--r-- 1 kms kms 20480 Jun 14 11:22 kms_bak_dsktstokms-3_vpc_cloudera_com_2023-06-14_11-22-42.tar
 -rw-r--r-- 1 kms kms   352 Jun 14 11:22 kt_bak_dsktstokms-3_vpc_cloudera_com_2023-06-14_11-22-42.log
 -rw-r--r-- 1 kms kms 20480 Jun 15 03:20 kms_bak_dsktstokms-3_vpc_cloudera_com_2023-06-15_03-20-54.tar
 -rw-r--r-- 1 kms kms   352 Jun 15 03:20 kt_bak_dsktstokms-3_vpc_cloudera_com_2023-06-15_03-20-54.log
  drwxr-xr-x 3 kms kms    55 Jun 15 03:21 keytrustee
 -rw-r--r-- 1 kms kms 10401 Jun 15 03:34 deposits.csv
If you want to migrate the KMS hosts, then also copy themigratedKeyStore.jceksfile to the Ranger KMS node.# scp root@dsktstokms-4.vpc.cloudera.com:/var/lib/keytrustee/.keytrustee/migratedKeyStore.jceks /var/lib/kms-keytrustee/keytrustee #ls -ltr /var/lib/kms-keytrustee/keytrustee -rw-r--r-- 1 kms kms 1210 Jun 15 03:21 migratedKeyStore.jceks -
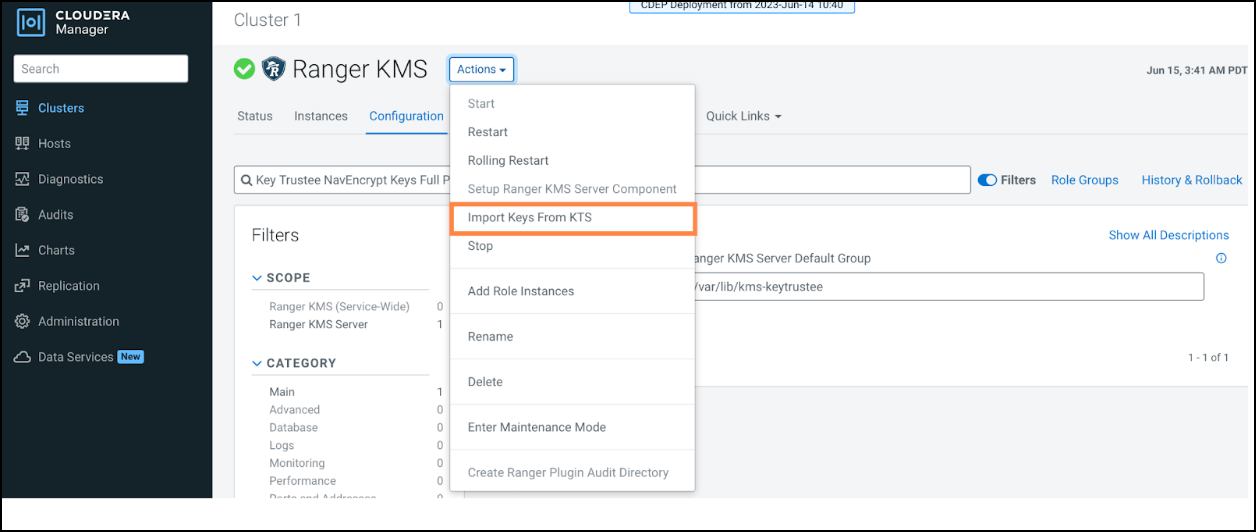
Import the keys from the keystore file and deposits.csv
file for NavEncrypt.
-
Go to and select
-
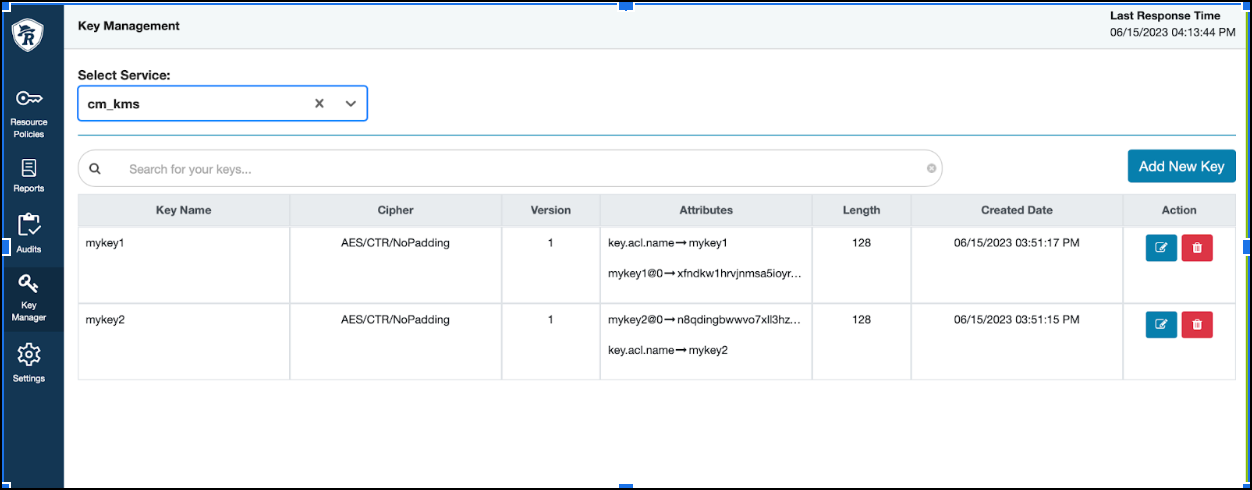
Go to and select
 # mysql -u root -p

 MariaDB [(none)]> use rangerkms;

 MariaDB [rangerkms]> show tables;
                +---------------------+
                | Tables_in_rangerkms |
                +---------------------+
                | navencrypt_deposit  |
                | ranger_keystore     |
                | ranger_masterkey    |
                +---------------------+
                3 rows in set (0.00 sec)